Short version, before you scroll: OpenClaw can be used safely, but the default way most people install it is seriously risky, and a lot of the “just run this command” tutorials skip the part where things can go very wrong. So let’s do the part they skip.
The honest one-liner
OpenClaw isn’t malware. It’s a legitimate open-source project run by a non-profit foundation. The danger isn’t the app itself. It’s what the app is allowed to do, and who else has learned to abuse that.
Remember the eager intern with the keys to your laptop? Same intern. This is the chapter where we talk about what happens when someone slips the intern a fake instruction. (New here? Start with What Is OpenClaw?)
Scare #1: the one-click hack
In early 2026, security researchers found a serious flaw in OpenClaw — officially CVE-2026-25253, rated 8.8 out of 10 on the industry severity scale (that’s “drop everything and patch” territory).
In plain English: if your OpenClaw was reachable from the internet, a single malicious link could let a stranger run commands on your machine. Not “see your data” — run commands. On a tool that’s already wired into your email, files, and messages.
It’s been patched. But it tells you the shape of the risk: when powerful software has a bug, the bug inherits all that power.
Scare #2: the poisoned add-on store
This is the big one, and it’s worse than a single flaw.
OpenClaw lets you install community-made “Skills” — little add-ons that teach it new tricks — from a store called ClawHub. Sounds great. Except security firm Koi Security audited all 2,857 Skills in the store and found 341 of them were malicious, roughly 1 in 8.
What did the bad ones do? They quietly installed an info-stealer (a nasty piece of malware-for-hire called AMOS) that hunts for exactly the things you don’t want stolen: browser passwords, saved logins, SSH keys, and crypto wallets. More than 100 of the fake Skills disguised themselves as crypto tools — think fake Solana or Phantom wallet helpers — aimed straight at people holding cryptocurrency.
The really uncomfortable detail: the attackers specifically targeted people running OpenClaw 24/7 on an always-on machine, which is exactly what enthusiasts are told to do. The setup that makes it most useful is also the one that makes it the juiciest target.
Why it’s riskier than a normal app
A normal app runs in its own little box and asks before it touches your stuff. OpenClaw is the opposite by design: you give it broad access so it can actually be useful. That’s the whole point, and the whole problem. When you hand something that much power, a single bad add-on or bad link doesn’t cause a small mess. It causes a big one.
There’s also no safety net you’d expect from a big company: as of early 2026, OpenClaw had no bug-bounty program and no dedicated security team. It’s volunteers moving fast. Big enterprise security firms have flagged it as a serious insider-threat risk for exactly this reason.
So can you actually use it safely? Yes — with rules.
If you still want to play with it (and honestly, it’s a fascinating toy), don’t install it on your everyday laptop. Do this instead:
- Update it the moment an update appears. This is rule number one for a reason. The 8.8 hack from Scare #1 was killed by a patch, and the people who got burned were running old versions. Boring, unglamorous, and the single most effective thing you can do.
- Run it on a separate machine: a cheap cloud server (VPS), a virtual machine, or an old spare laptop that holds nothing sensitive. Never your main device. (Heads up: a VPS is on the internet by default, so the “keep it off the open internet” rule below isn’t optional there.)
- Never run it as the “root” / admin user. If it gets tricked, you want it to have as little power as possible.
- Keep it off the open internet. There’s a setting that binds it to your own machine only (
127.0.0.1instead of0.0.0.0). Turn that on. It won’t fix a bad update, but it keeps random internet strangers from finding your instance in the first place. - Treat every community Skill like a stranger’s USB stick. Check who made it, look at the code if you can, and never install one that asks for more access than its job needs.
- Keep zero crypto keys and passwords on that machine. If there’s nothing to steal, a stealer goes home empty-handed.
Who should just walk away
If you’re not comfortable spinning up a spare machine and toggling security settings, that’s not a failure — it’s good judgment. OpenClaw is currently a power-user’s toy with power-user’s risks. For “I just want AI to help with everyday stuff,” a normal chatbot in your browser gives you 90% of the benefit and roughly none of this headache.
The bottom line
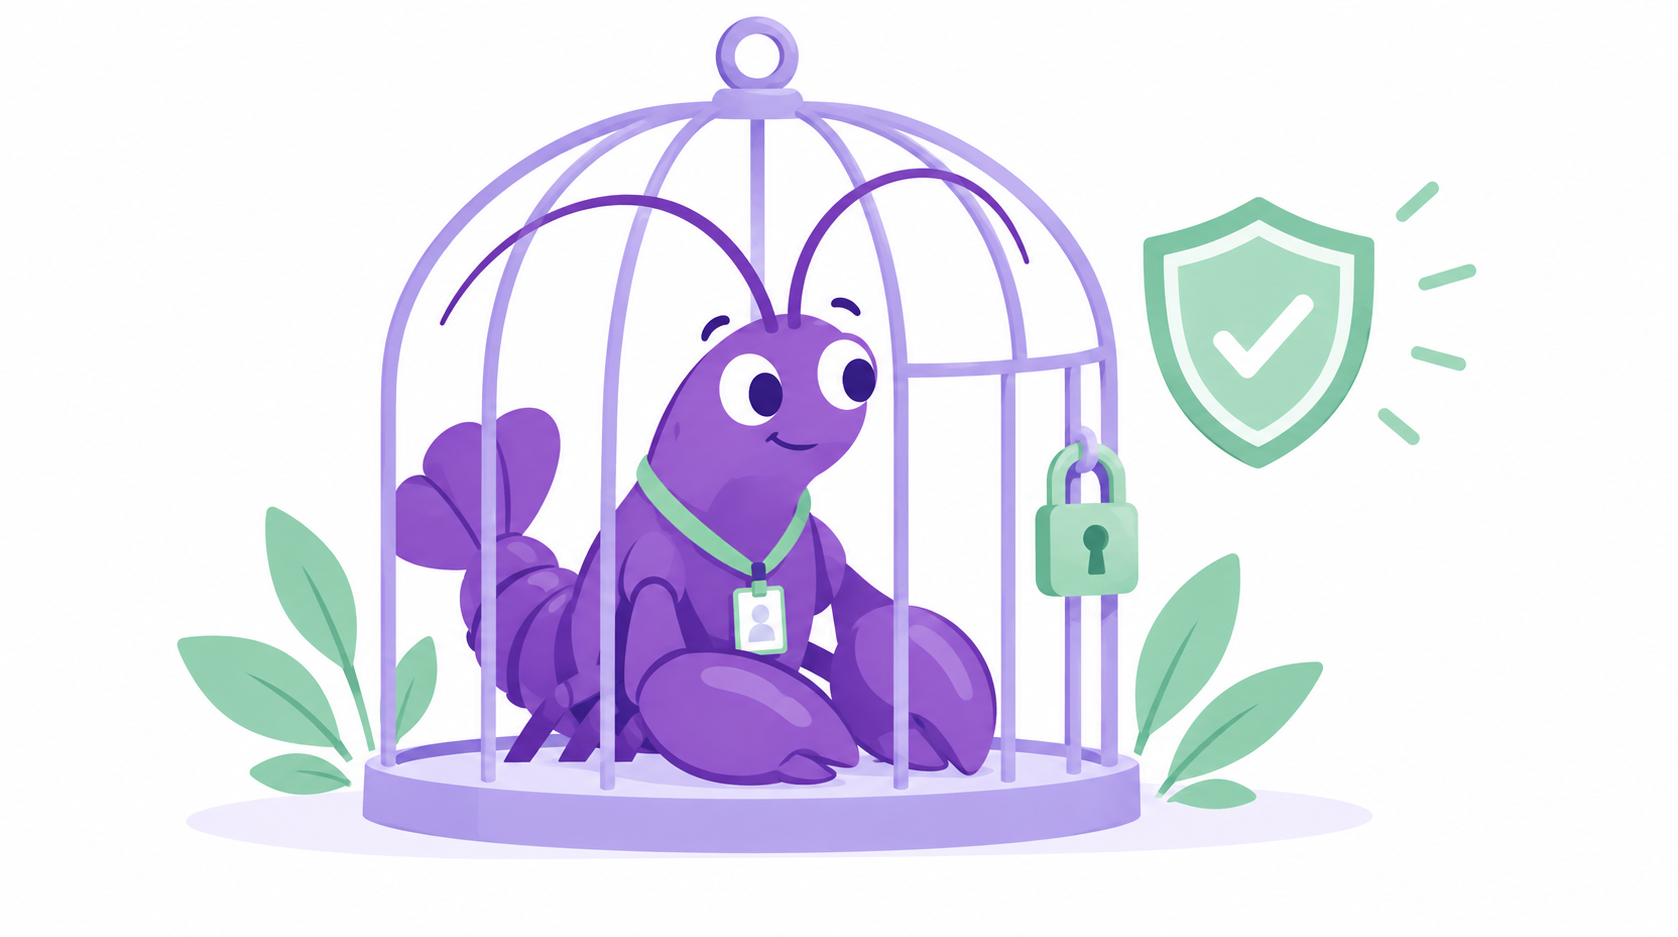
OpenClaw is safe if you cage it: updated, on a separate machine, low privileges, off the open web, no valuables inside, and a deep suspicion of community add-ons. Run it that way and it’s a genuinely cool experiment. Run it on your main laptop with the store wide open, and you’re the target the whole story was warning you about.
Wondering how it stacks up against a tool that does come with guardrails? Read OpenClaw vs Claude Code →.